An ISMS you can actually run
Xelon is an implementation partner for Base27, the European-hosted ISMS platform.
The hardest part of ISO 27001 is not getting the certificate. It is operating the management system afterwards. In most organisations the ISMS ends up scattered across SharePoint folders, spreadsheets and someone's inbox, and every surveillance audit becomes an archaeology project. The system exists on paper but nobody could honestly say where the current version of anything lives.
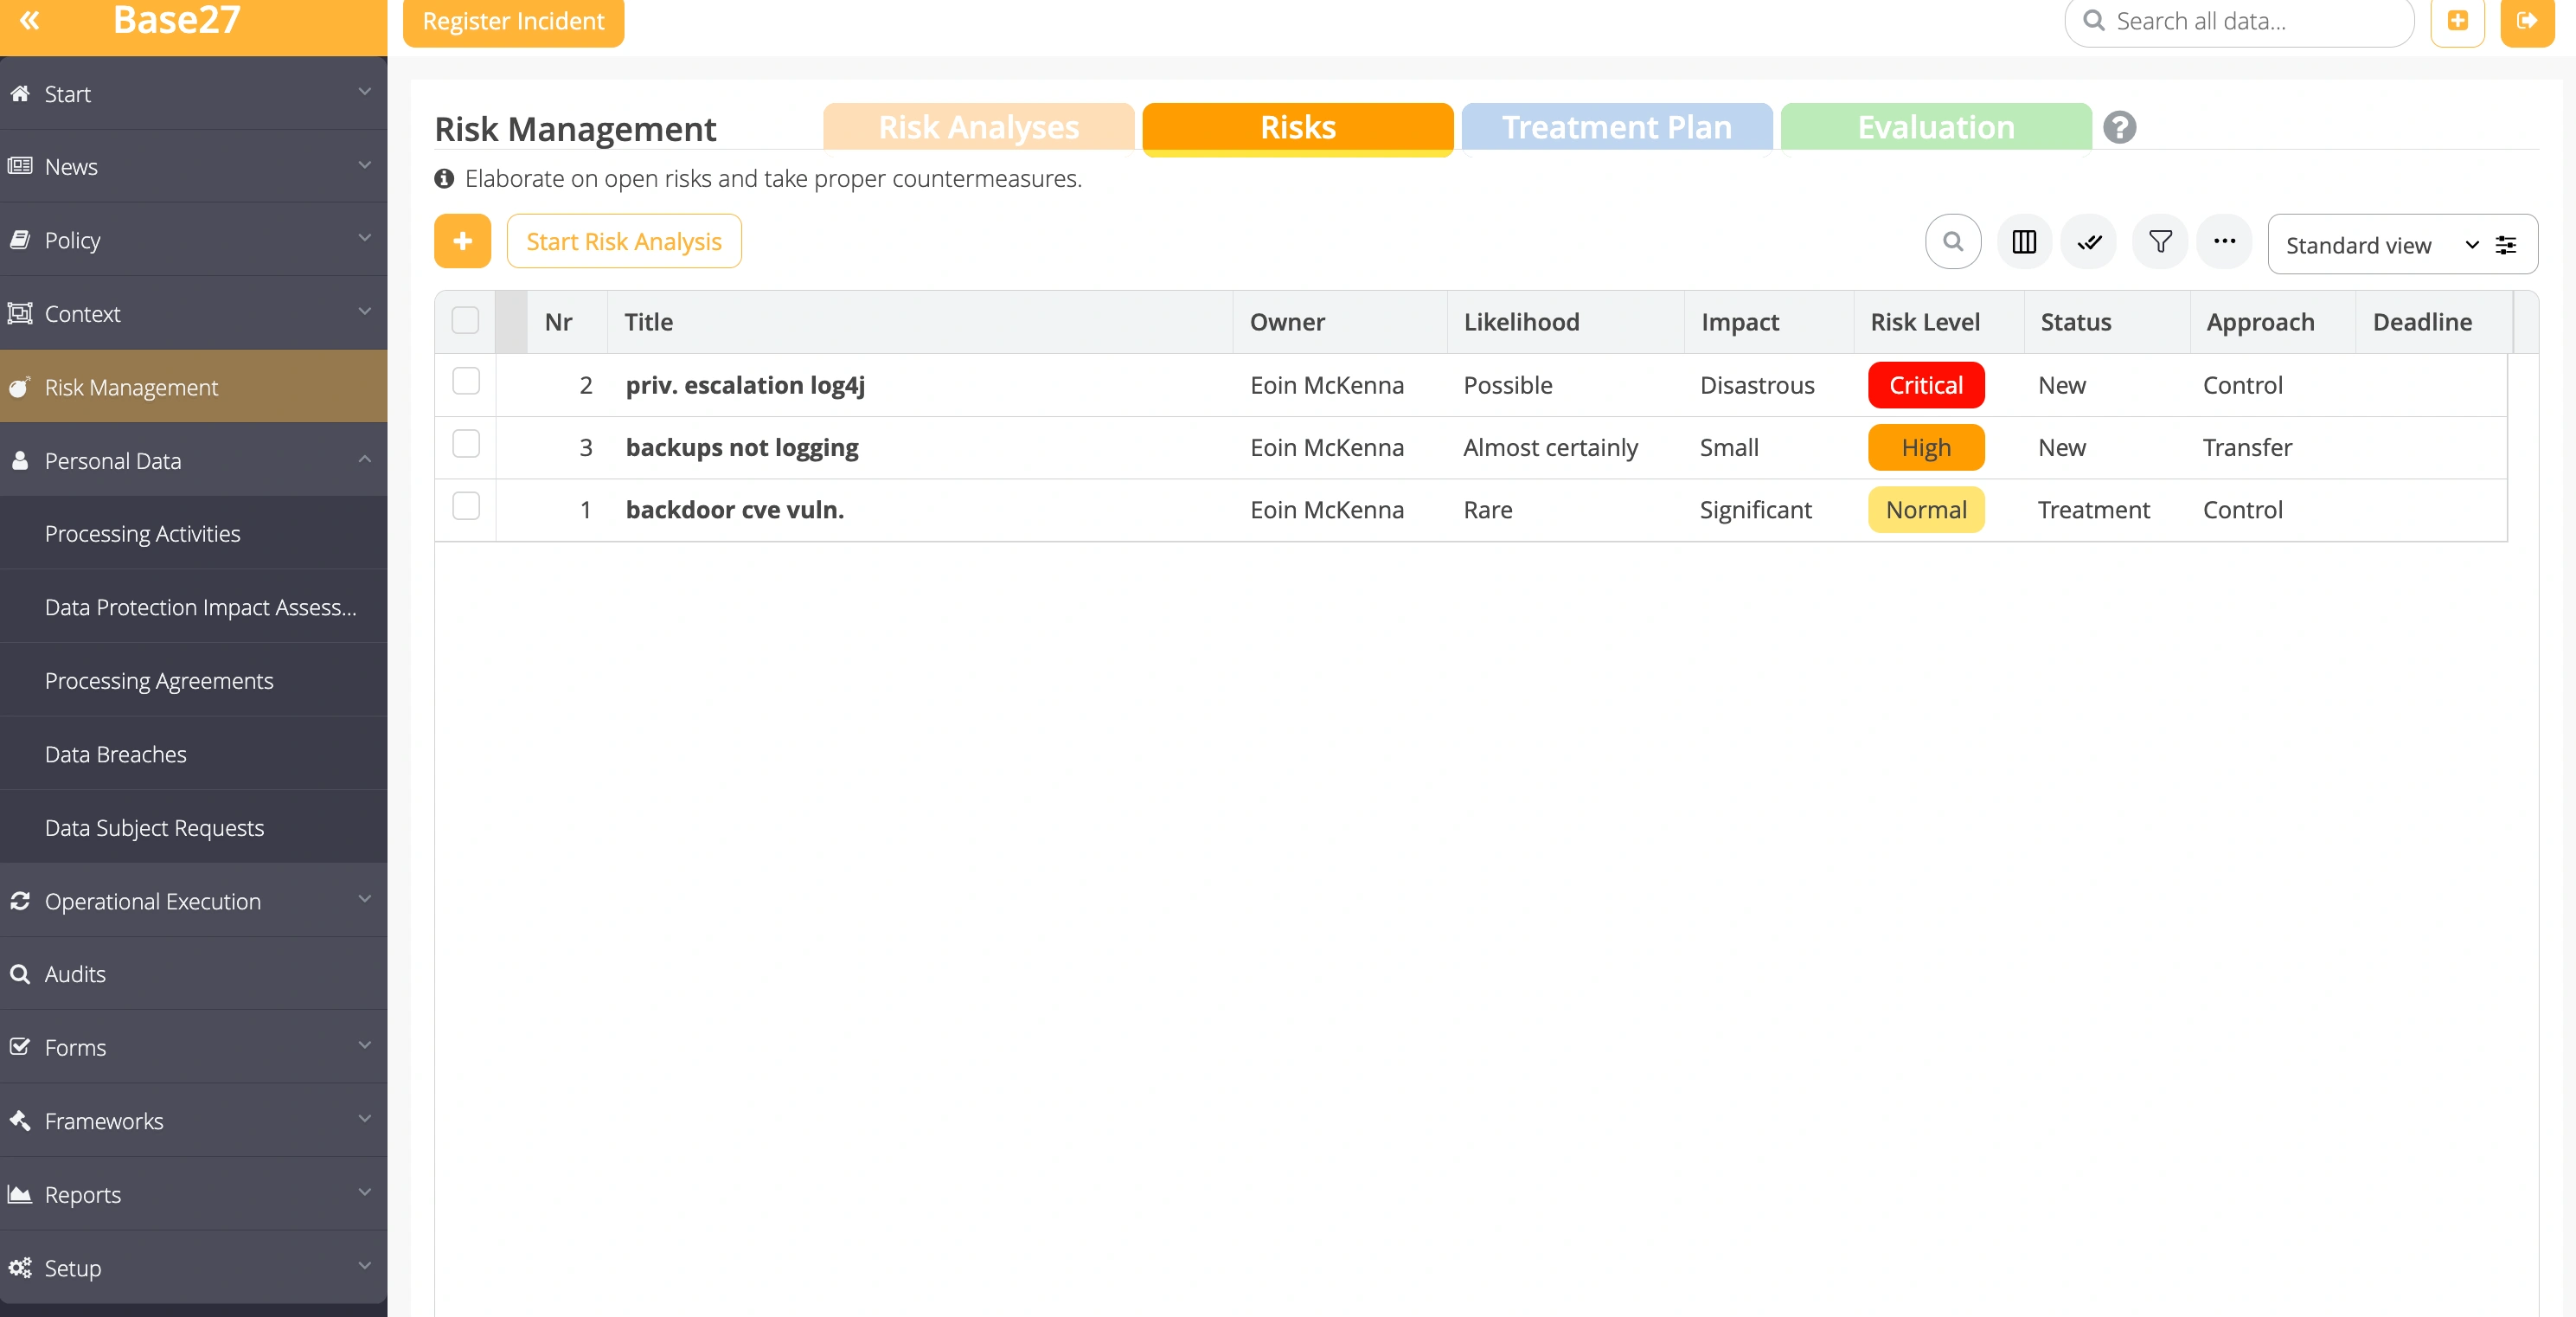
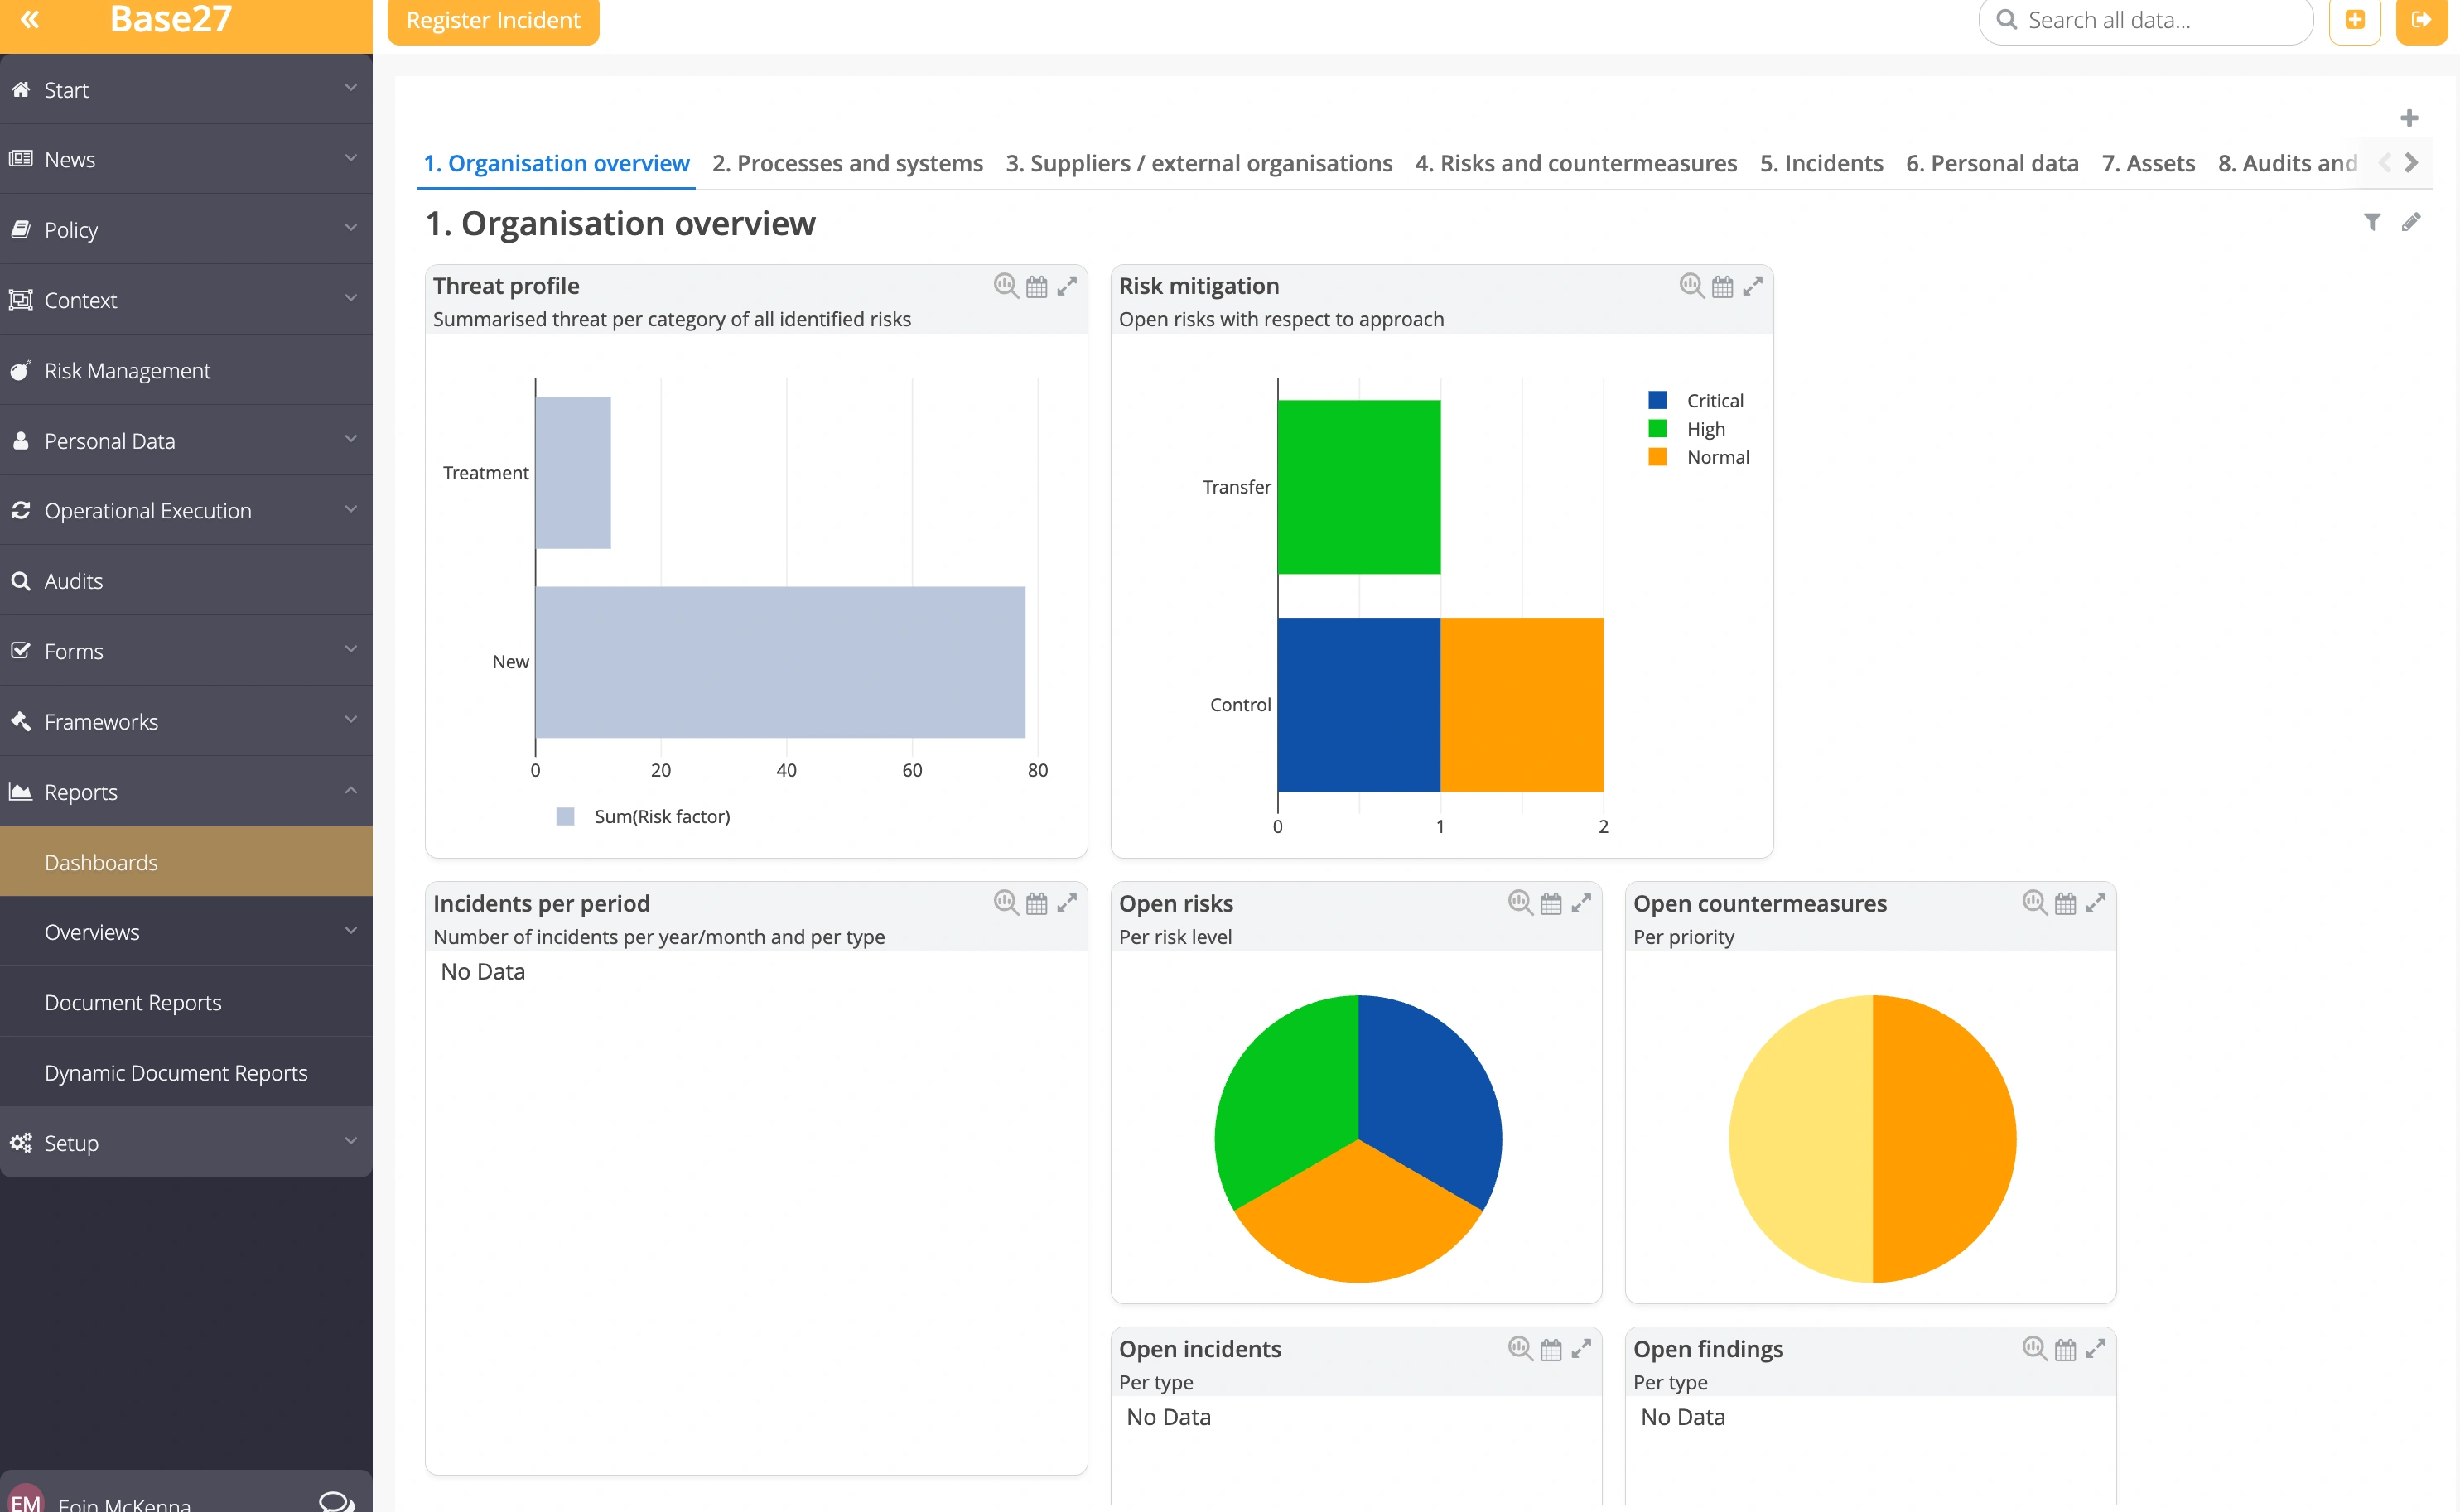
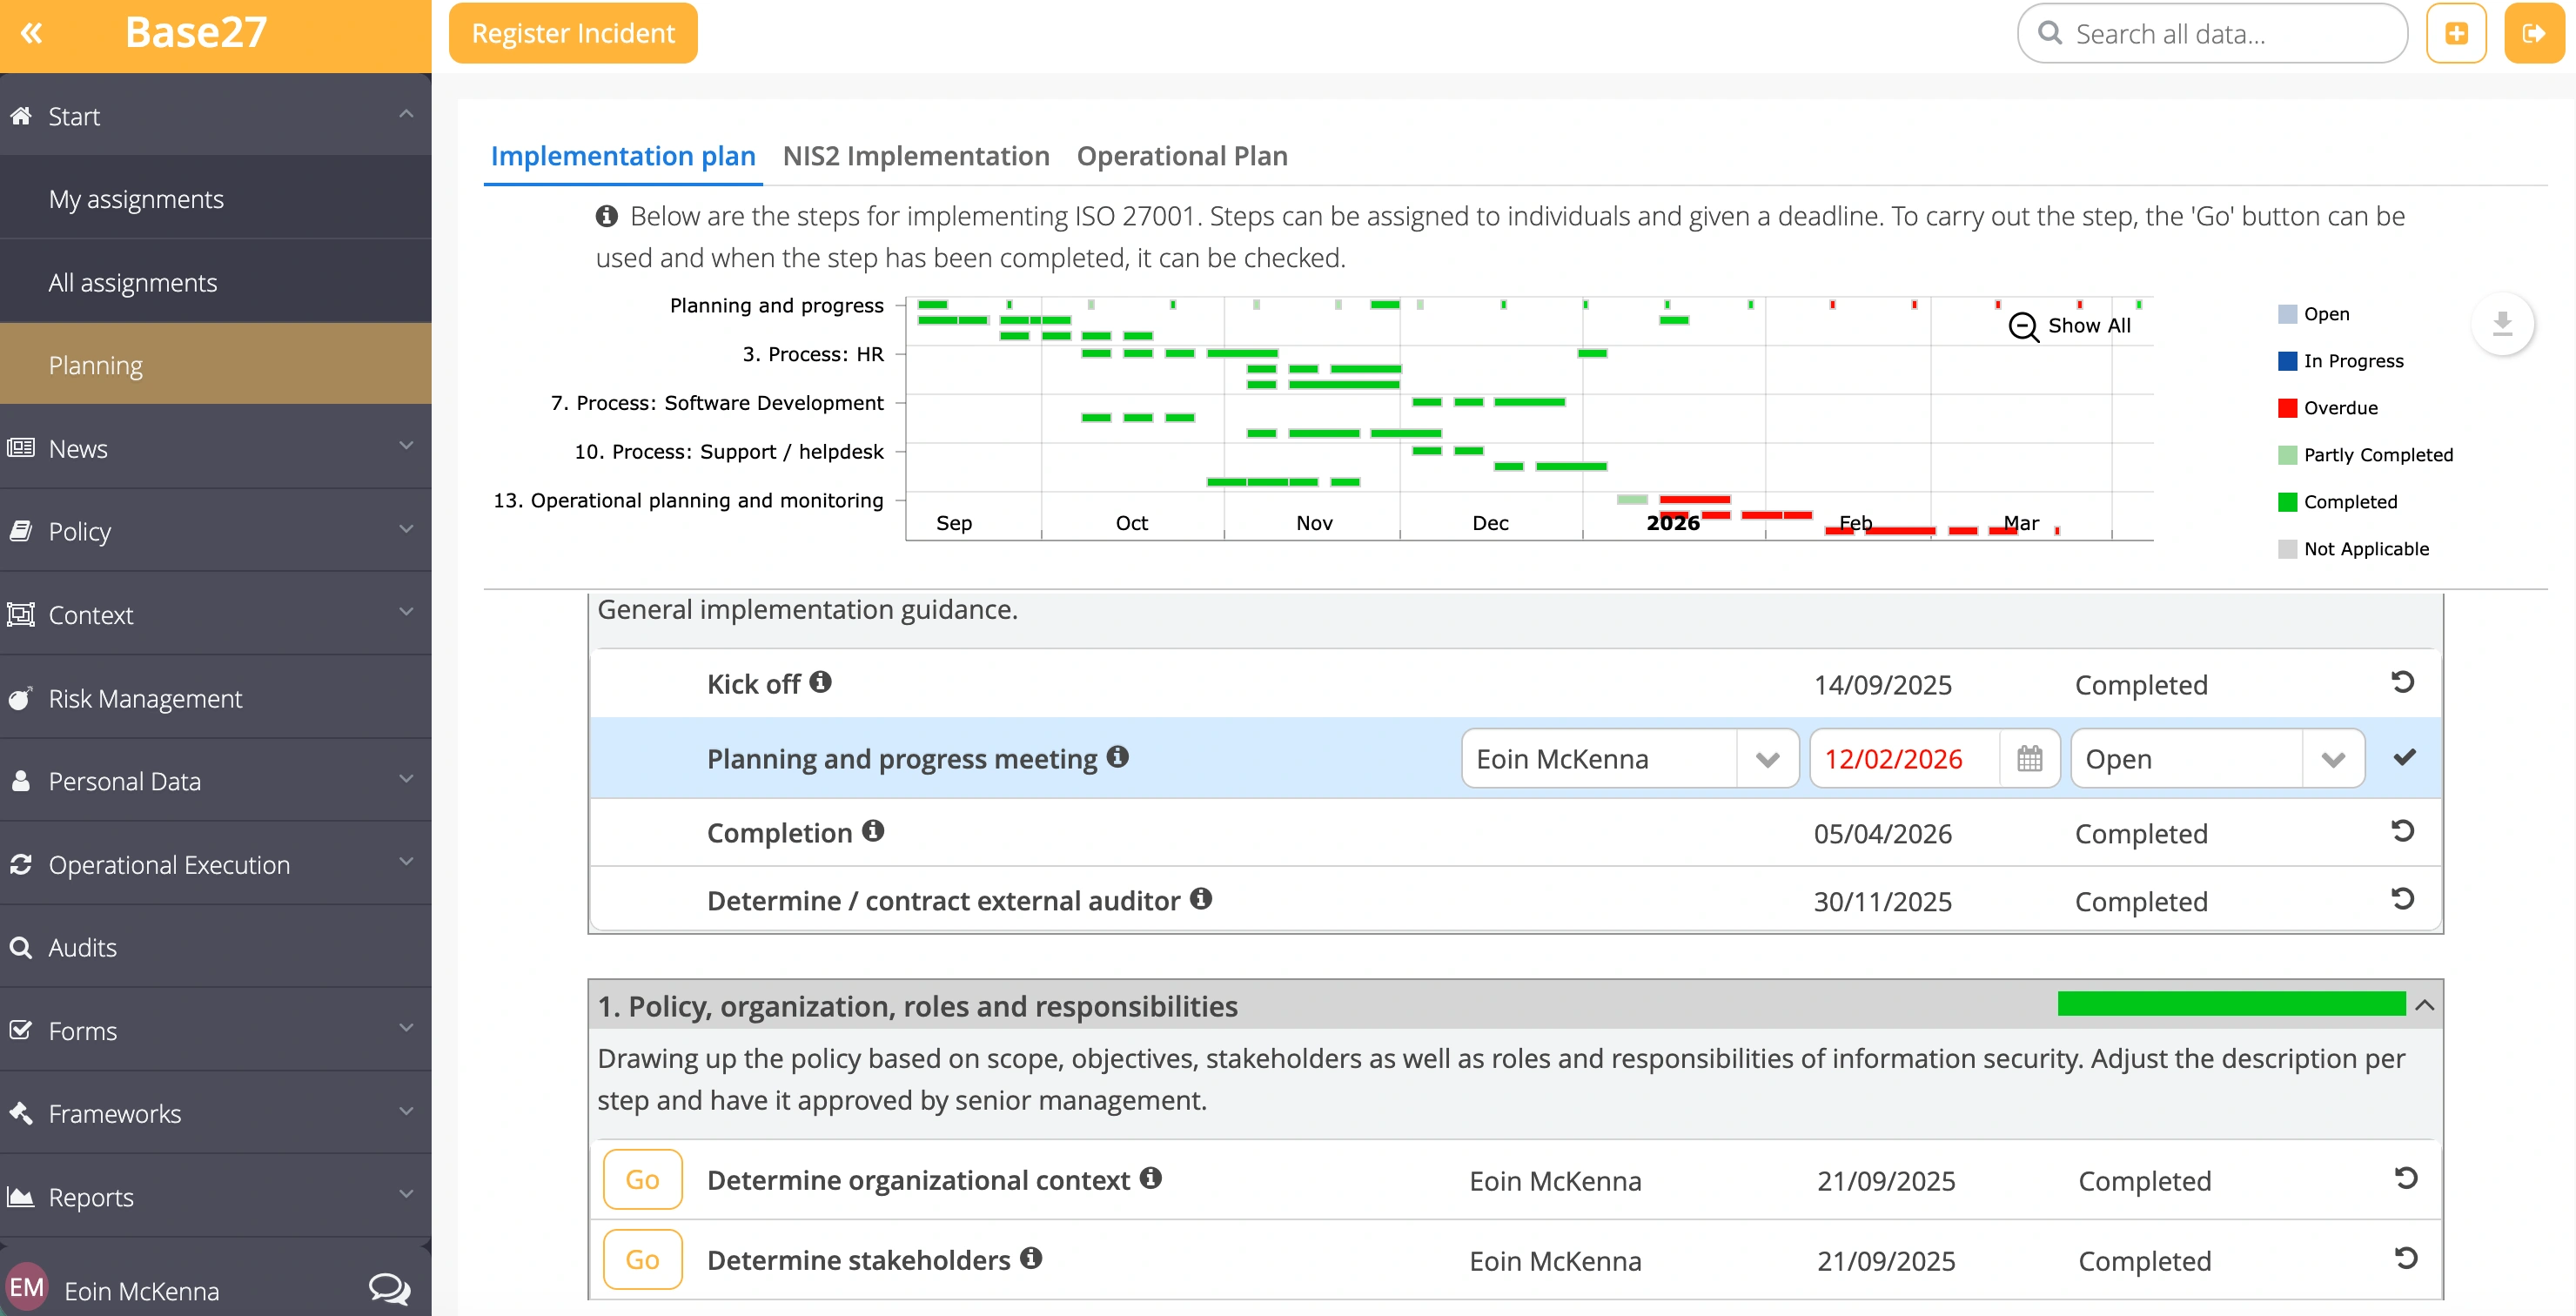
Base27 fixes that. It is an online ISMS platform built by Axxemble, hosted in Europe, that holds your policies, risk assessments, controls, audit programme and evidence in one place, directly linked to the frameworks you are certifying against. It supports more than 75 standards including ISO 27001, ISO 27701 and GDPR, and ISO 9001, comes with a full policy framework and implementation plan built in, and integrates with your environment through single sign-on and a REST API. When the auditor asks for your Statement of Applicability, your risk register or the evidence behind a control, it is one click, not one week.
Why we partner with Base27
Xelon remains vendor-neutral across our advisory services. Base27 is the exception, and a deliberate one: after implementing the platform in a large and complex Irish public sector environment, migrating dozens of risks with their countermeasures out of a legacy internal application and into a structure that carried through to certification audit, we chose to become an implementation partner. Attaching our name to a product is not something we do lightly. Base27 earned it in live use. We know where the platform is strong, where it needs configuring with care and how to make it fit an Irish organisation rather than forcing the organisation to fit the tool.
What we deliver
We set up Base27 around your certified scope rather than a generic template, migrate your existing policies, risks and controls into it, and map your control set to the frameworks that matter to you, whether that is ISO 27001 alone or ISO 27001 alongside NIS2 obligations. We train your security officers and staff so the platform becomes part of how the organisation works, and we can support the ongoing cycle of internal audits, management reviews and continual improvement that keeps both the certificate and the system alive. If your ISMS currently lives in a binder, we will get it breathing.