Security architecture and technical advisory
Vendor-neutral design and oversight, by people who have built what they recommend.
Xelon is a consultancy, not a managed service provider, and that independence is precisely why clients bring us in. We design, review and oversee, which means our advice on architecture and tooling is never shaped by what we happen to sell. Our practitioners have spent decades hands-on with Cisco networking and security platforms, Microsoft 365 and Azure, so the designs we produce are ones we could implement ourselves.
Architecture review
An independent assessment of your identity, network and cloud security architecture, identifying the weaknesses an attacker would find and the complexity that is costing you money without buying you protection.
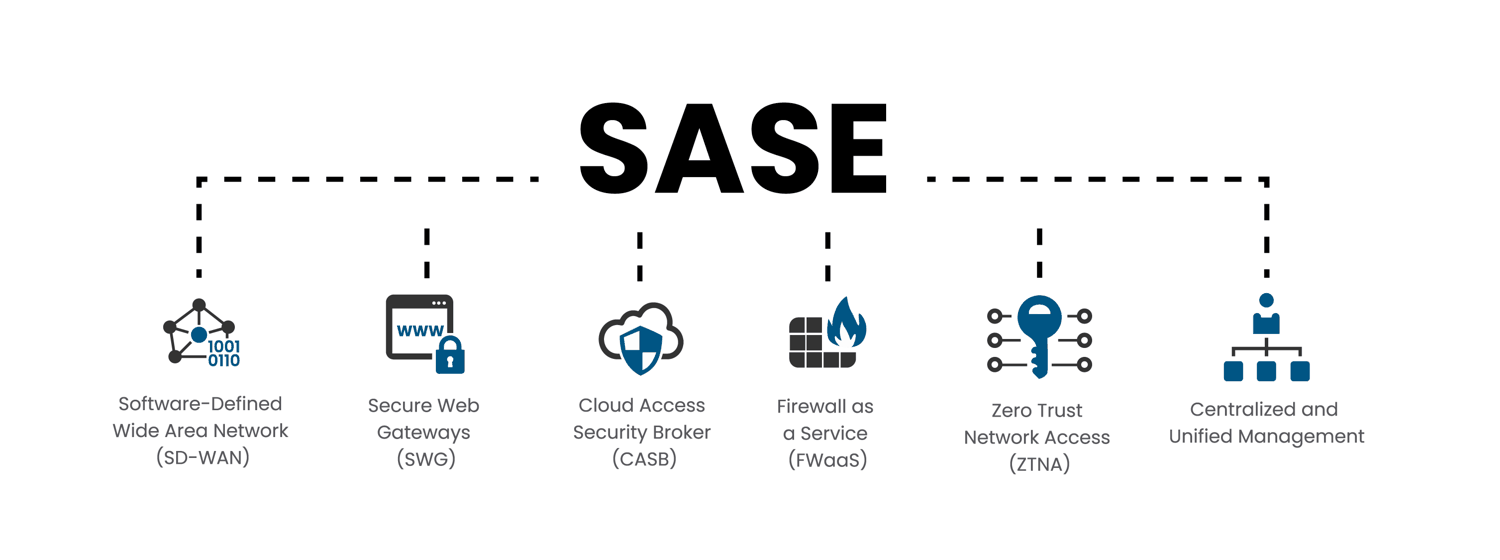
SASE and secure remote access
We help organisations replace ageing VPN and legacy remote access estates with modern cloud-delivered secure access, designed around how your workforce actually operates rather than around a vendor's licence bundle. That includes requirements definition, vendor evaluation, migration planning and design assurance during rollout.
Network segmentation
Zoning and segmentation designs that contain an incident to the system where it starts, protecting critical services while the rest of the business keeps operating. We have delivered segmentation work in environments where downtime is politically visible and the design has to be right the first time.
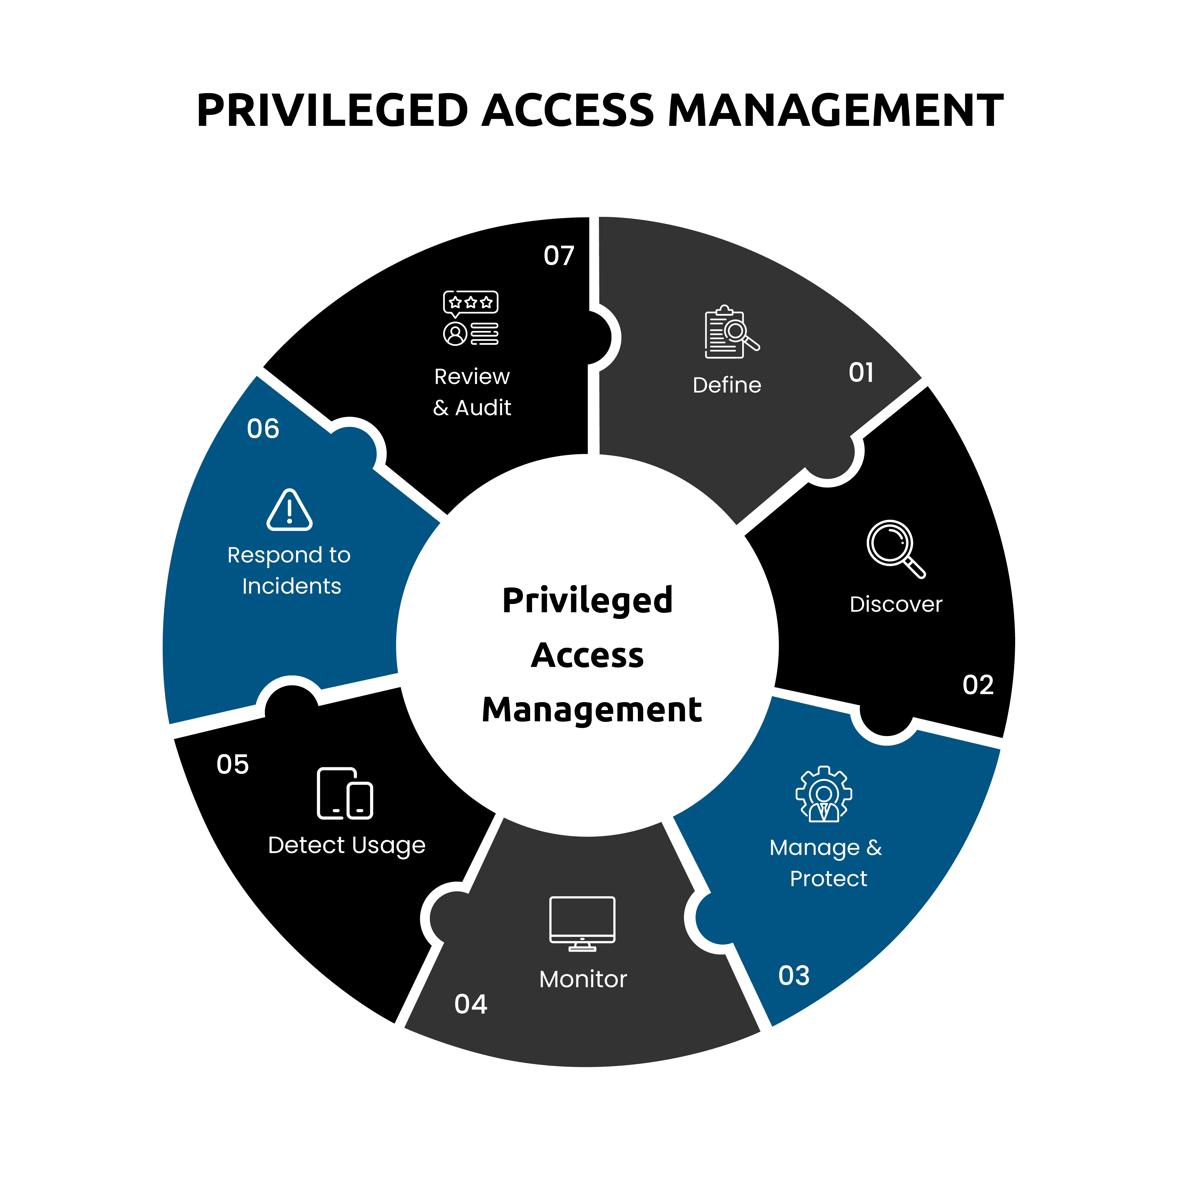
Privileged access management
Governance frameworks for privileged, generic and service accounts, and implementation oversight for PAM platforms integrated with existing network access control. We have designed and overseen deployments involving BeyondTrust and Cisco ISE, and we can tell you honestly whether you need a platform at all or just better discipline.
Threat and vulnerability management
We build TVM programmes that actually reduce exposure: scanning coverage, exploitability-based triage, hardening and decommissioning of legacy servers, and the recurring review cadence that keeps remediation moving. We will chair those calls if you want us to.